01
Assess
Deep-dive audits, inventory, GAP analysis and AI readiness reviews. We establish what exists, what is exposed, which AI tools are in play, and what the business actually needs before anyone buys another box.
Approach
A method built for continuity - not a one-off project that evaporates after handover.
Deep-dive audits, inventory, GAP analysis and AI readiness reviews. We establish what exists, what is exposed, which AI tools are in play, and what the business actually needs before anyone buys another box.
Customised networking and security design - security switches, segmentation, routing and access paths. Architecture is planned for the next three to five years of scale, not just the current floor plan, with CISSP / (ISC)² control thinking in the blueprint.
Seamless deployment of hardware, security switches, networking and controls. The intent is continuity - disciplined cutovers, documented racks, and systems people can run.
Continuous improvement, monitoring readiness and resilience. Security is a programme: reviews, hardening and a remediation path that stays owned.
Architecture
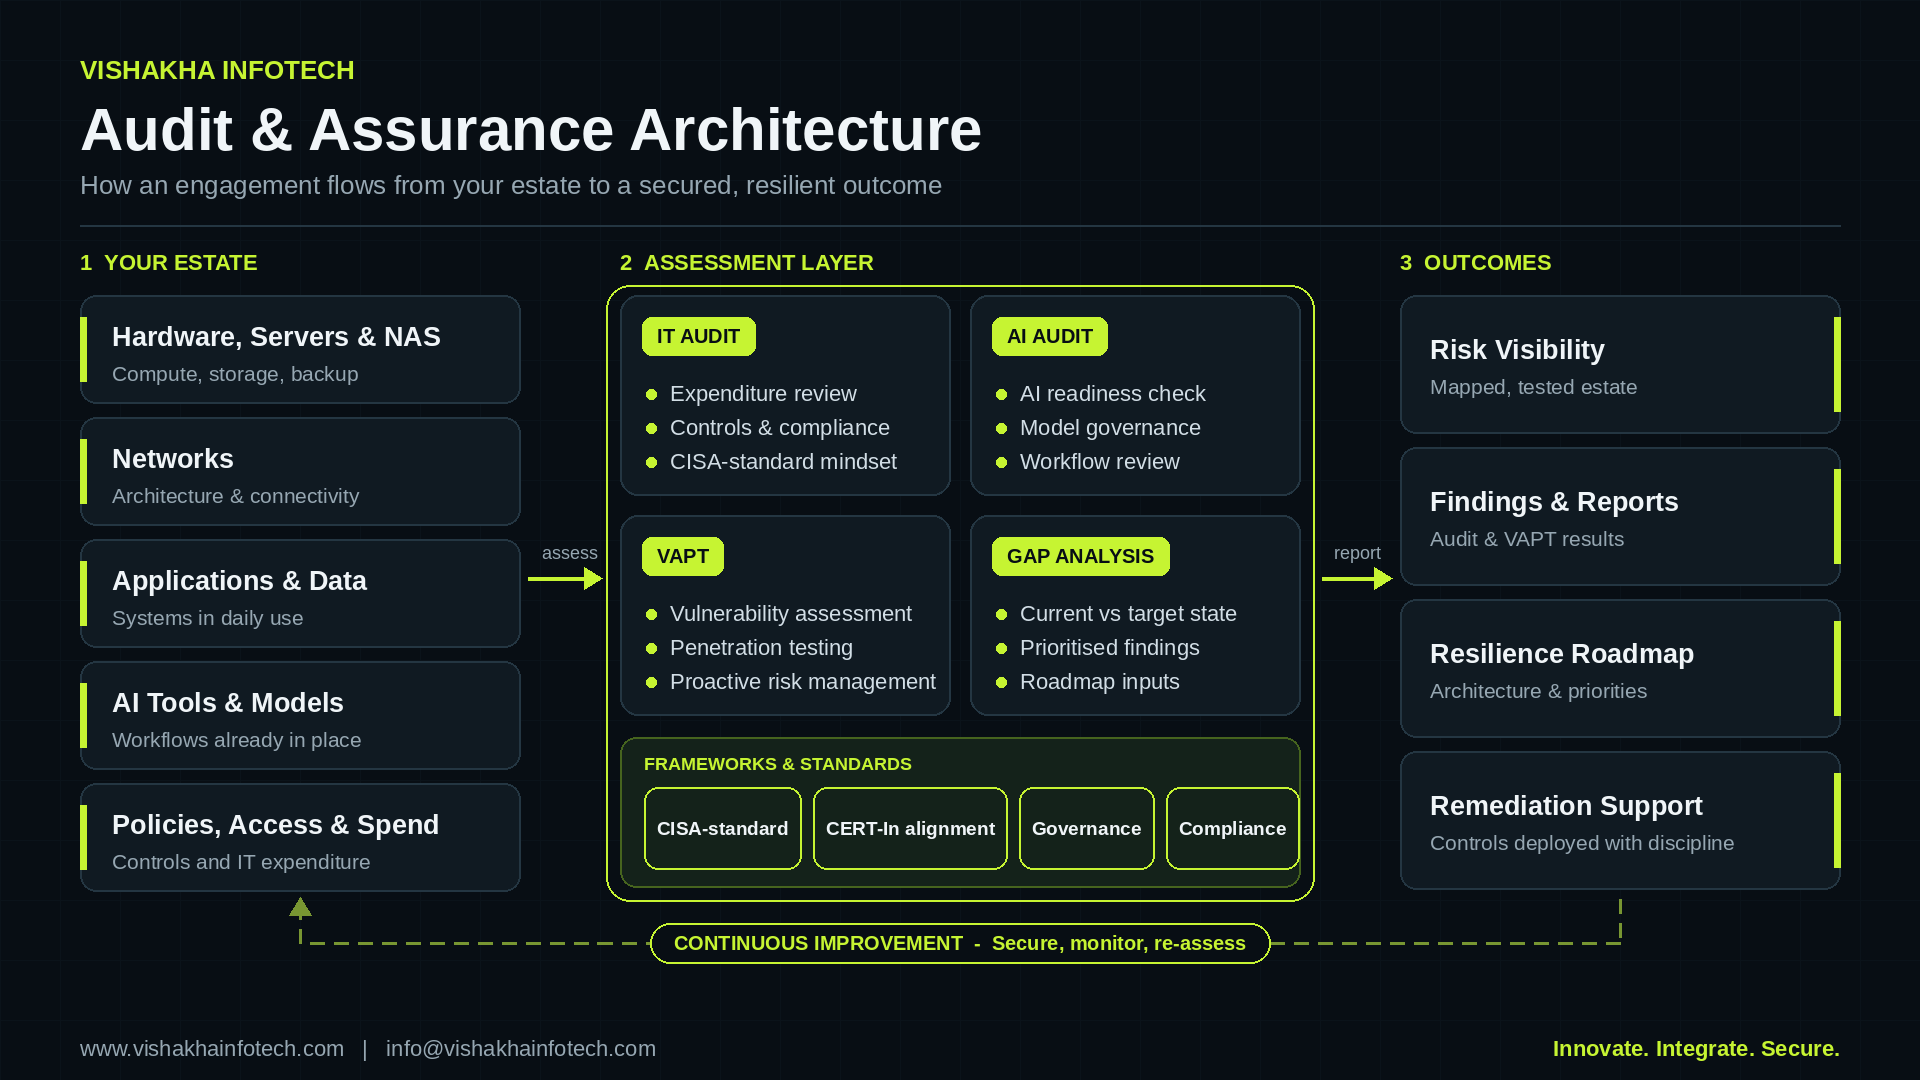
How an engagement moves from your estate through assessment - IT audit, AI audit, VAPT and GAP analysis - into clear outcomes and continuous improvement.
Advantage
From hardware to security audits and AI system reviews, we coordinate the work end to end. You are not handed between vendors for every layer of the stack.
Solutions planned for scalability over the next three to five years - capacity, documentation and security controls included.
Clear documentation, actionable findings and prioritised next steps. Reports written for operators and leadership, not for a drawer.
Local consulting presence with enterprise-grade delivery discipline. On the ground when the rack, the audit or the incident needs it.
We begin where every resilient programme should: with a clear picture of the estate.